0633
A member of the human resources department received the following email message after sending an email
containing benefit and tax information to a candidate:
"Your message has been quarantined for the following policy violation: external potential_PII. Please contact the IT
security administrator for further details".
Which of the following BEST describes why this message was received?
Answer
The DLP system flagged the message.
The mail gateway prevented the message from being sent to personal email addresses.
The company firewall blocked the recipient's IP address.
The file integrity check failed for the attached files.
Card 22
Question
0697
A salesperson often uses a USB drive to save and move files from a corporate laptop. The coprorate laptop was
recently updated, and now the files on the USB drive are read-only. Which of the following was recently added to
the laptop?
Answer
Antivirus software
File integrity check
HIPS
DLP
Card 23
Question
0746
An organization's research department uses workstations in an air-gapped network. A competitor released
products based on files that originated in the research department. Which of the following should management do
to improve the security and confidentiality of the research files?
Answer
Configure removable media controls on the workstations.
Implement multifactor authentication on the workstations.
Install a web application firewall in the research department.
Install HIDS on each of the research workstations.
Card 24
Question
0754
A security administrator receives alerts from the perimeter UTM. Upon checking the logs, the administrator finds
the following output:
Time: 12/25 0300
From Zone: Untrust
To Zone: DMZ
Attacker: externalip.com
Victim: 172.16.0.20
To Port: 80
Action: Alert
Severity: Critical
When examining the PCAP associated with the event, the security administrator finds the following information:
<script>alert("Click here for important information regarding your account! http://
externalip.com/account.php");</script>
Which of the following actions should the security administrator take?
Answer
Upload the PCAP to the IDS in order to generate a blocking signature to block the traffic.
Implement a host-based firewall rule to block future events of this type from occurring.
Manually copy the
Submit a change request to modify the XSS1 vulnerability signature to TCP reset on future attempts.
Card 25
Question
0762
A company recently implemented a new security system. In the course of configuration, the security administrator
adds the following entry:
#Whitelist USB\VID_13FE&PID_4127&REV_0100
Which of the following security technologies is MOST likely being configured?
Answer
Application whitelisting
HIDS
Removable media control
Data execution prevention
Card 26
Question
0797
A security analyst is interested in setting up an IDS to monitor the company network. The analyst has been told
there can be no network downtime to implement the solution, but the IDS must capture all of the network traffic.
Which of the following should be used for the IDS implementation?
Answer
Network tap
Honeypot
Aggregation
Port mirror
Card 27
Question
0799
A systems administrator is receiving multiple alerts from the company NIPS. A review of the NIPS logs shows the
following:
The company web server was attacked by an external source, and the NIPS blocked the attack.
The company web and SQL servers suffered a DoS caused by a misconfiguration of the NIPS
An external attacker was able to compromise the SQL server using a vulnerable web application.
The NIPS should move from an inline mode to an out-of-band mode to reduce network latency.
Card 28
Question
0825
An organization plans to transition the intrusion detection and prevention techniques on a critical subnet to an
anomaly-based system.
Which of the following does the organization need to determine for this to be successful?
Answer
The baseline
The endpoint configurations
The adversary behavior profiles
The IPS signatures
Card 29
Question
0910
A Security analyst has received an alert about Pll being sent via email. The analyst's Chief Information Security
Officer (CISO) has made it clear that Pll must be handled with extreme care. From which of the following did the
alert MOST likely originate?
Answer
S/MIME
IMAP
DLP
HIDS
Card 30
Question
0927
A company has drafted an Insider-threat policy that prohibits the use of external storage devices. Which of the
following would BEST protect the company from data exfiltration via removable media?
Answer
Monitoring large data transfer transactions in the firewall logs
Developing mandatory training to educate employees about the removable media policy
Implementing a group policy to block user access to system files
Blocking removable-media devices and write capabilities using a host-based security tool
Card 31
Question
0928
A network administrator has been asked to install an IDS to improve the security posture of an organization. Which
of the following control types is an IDS?
Answer
Corrective
Administrative
Detective
Physical
Card 32
Question
0955
After patching computers with the latest application security patches/updates, users are unable to open certain
applications. Which of the following will correct the issue?
Answer
Modifying the security policy for patch management tools
Modifying the security policy for HIDS/HIPS
Modifying the security policy for DLP
Modifying the security policy for media control
Card 33
Question
0969
A technician needs to prevent data loss in a laboratory. The laboratory is not connected to any external networks.
Which of the following methods would BEST prevent the exfiltration of data? (Select TWO).
Answer
VPN
Drive encryption
Network firewall
File-level encryption
USB blocker
MFA
Card 34
Question
0991
A company is having issues with intellectual property being sent to a competitor from its system. The information
being sent is not random but has an identifiable pattern.
Which of the following should be implemented in the system to stop the content from being sent?
Answer
Hashing
IPS
Encryption
DLP
Card 35
Question
0995
An organization is struggling to differentiate threats from normal traffic and access to systems. A security engineer
has been asked to recommend a system that will aggregate data and provide metrics that will assist in identifying
malicious actors or other anomalous activity throughout the environment.
Which of the following solutions should the engineer recommend
Answer
Web application firewall
SIEM
IPS
UTM
File integrity monitor
Card 36
Question
0997
Joe, a user at a company, clicked an email link that led to a website that infected his workstation. Joe was
connected to thenetwork, and the virus spread to the network shares. The protective measures failed to stop this
virus, and it has continued to evade detection.
Which of the following should a security administrator implement
to protect the environment from this malware?
Answer
Install a definition-based antivirus.
Implement an IDS/IPS.
Implement a heuristic behavior-detection solution.
Implement CASB to protect the network shares.
Card 37
Question
1007
Which of the following control types are alerts sent from a SIEM fulfilling based on vulnerability signatures?
Answer
Preventive
Corrective
Compensating
Detective
Card 38
Question
1010
An analyst has determined that a server was not patched and an external actor exfiltrated data on port 139.
Which of the following sources should the analyst review to BEST ascertain how the incident could have been prevented?
Answer
The security logs
The vulnerability scan output
The baseline report
The correlation of events
Card 39
Question
0833
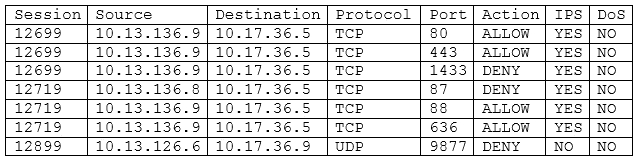
The application team within a company is asking the security team to investigate why its application is slow after an upgrade. The source of the team's application is 10.13.136.9, and the destination IP is 10.17.36.5. The security analyst pulls the logs from the endpoint security software but sees nothing is being blocked. The analyst then looks at the UTM firewall logs and sees the following:
Which of the following should the security analyst request NEXT based on the UTM firewall analysis?
Answer
Request the application team to allow TCP port 87 to listen on 10.17.36.5.
Request the network team to open port 1433 from 10.13.136.9 to 10.17.36.5.
Request the network team to turn off IPS for 10.13.136.8 going to 10.17.36.5.
Request the application team to reconfigure the application and allow RPC communication.
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.