All questions without description (e.g. Question #1) are from the premium version of Exam Topics. I always choosed the community answer if possible for them. The rest is from the specific documents, written in the header of each question.
A high volume of failed RDP authentication attempts was logged on a critical server within a one-hour period. All of the attempts originated from the same remote IP address and made use of a single valid domain user account. Which of the following would be the most effective mitigating control to reduce the rate of success of this brute-force attack?
Answer
B. Installing a third-party remote access tool and disabling RDP on all devices
A. Enabling a user account lockout after a limited number of failed attempts
C. Implementing a firewall block for the remote system's IP address
D. Increasing the verbosity of log-on event auditing on all devices
Card 222
Question
Question #221
An incident response analyst is investigating the root cause of a recent malware outbreak. Initial binary analysis indicates that this malware disables host security services and performs cleanup routines on its infected hosts, including deletion of initial dropper and removal of event log entries and prefetch files from the host. Which of the following data sources would most likely reveal evidence of the root cause? (Choose two.)
Answer
B. Registry artifacts
C. EDR data
A. Creation time of dropper
F. Sysmon event log
D. Prefetch files
E. File system metadata
Card 223
Question
Question #222
When undertaking a cloud migration of multiple SaaS applications, an organization's systems administrators struggled with the complexity of extending identity and access management to cloud-based assets. Which of the following service models would have reduced the complexity of this project?
Answer
C. ZTNA
B. SASE
D. SWG
A. CASB
Card 224
Question
Question #223
A security analyst reviews the following extract of a vulnerability scan that was performed against the web server:
Which of the following recommendations should the security analyst provide to harden the web server?
Answer
D. Close port 22.
A. Remove the version information on http-server-header.
C. Delete the /wp-login.php folder.
B. Disable tcp_wrappers.
Card 225
Question
Question #224
A security analyst is responding to an incident that involves a malicious attack on a network data closet. Which of the following best explains how the analyst should properly document the incident?
Answer
A. Back up the configuration file for all network devices.
D. Take photos of the impacted items.
C. Create a full diagram of the network infrastructure.
B. Record and validate each connection.
Card 226
Question
Question #225
A cybersecurity analyst is participating with the DLP project team to classify the organization's data. Which of the following is the primary purpose for classifying data?
Answer
A. To identify regulatory compliance requirements
C. To prioritize IT expenses
D. To establish the value of data to the organization
B. To facilitate the creation of DLP rules
Card 227
Question
Question #226
A security analyst observed the following activity from a privileged account:
• Accessing emails and sensitive information
• Audit logs being modified
• Abnormal log-in times
Which of the following best describes the observed activity?
Answer
B. Unauthorized privileges
D. Insider attack
C. Rogue devices on the network
A. Irregular peer-to-peer communication
Card 228
Question
Question #227
A vulnerability management team found four major vulnerabilities during an assessment and needs to provide a report for the proper prioritization for further mitigation. Which of the following vulnerabilities should have the highest priority for the mitigation process?
Answer
A. A vulnerability that has related threats and IoCs, targeting a different industry
D. A vulnerability that is related to an isolated system, with no IoCs
B. A vulnerability that is related to a specific adversary campaign, with IoCs found in the SIEM
C. A vulnerability that has no adversaries using it or associated IoCs
Card 229
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #1
A security analyst received a malicious binary file to analyze. Which of the following is the best technique to perform the analysis?
Answer
B. Static analysis
D. Fuzzing
A. Code analysis
C. Reverse engineering
Card 230
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #2
An incident response team found IoCs in a critical server. The team needs to isolate and collect technical evidence for further investigation. Which of the following pieces of data should be collected first in order to preserve
sensitive information before isolating the server?
Answer
A. Hard disk
B. Primary boot partition
D. Routing table
C. Malicious tiles
E. Static IP address
Card 231
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #3
Which of the following security operations tasks are ideal for automation?
Answer
A. Suspicious file analysis: Look for suspicious-looking graphics in a folder. Create subfolders in the original folder based on category of graphics found. Move the suspicious graphics to the appropriate subfolde
B. Firewall IoC block actions: Examine the firewall logs for IoCs from the most recently published zero-day exploit Take mitigating actions in the firewall to block the behavior found in the logs Follow up on any false positives that were caused by the block rules
C. Security application user errors: Search the error logs for signs of users having trouble with the security application Look up the user's phone number Call the user to help with any questions about using the application
D. Email header analysis: Check the email header for a phishing confidence metric greater than or equal to five Add the domain of sender to the block list Move the email to quarantine
Card 232
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #6
Which of the following best describes the reporting metric that should be utilized when measuring the degree to which a system, application, or user base is affected by an uptime availability outage?
Answer
A. Timeline
B. Evidence
C. Impact
D. Scope
Card 233
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #9
Which of the following best describes the key elements of a successful information security program?
Answer
A. Business impact analysis, asset and change management, and security communication plan
C. Disaster recovery and business continuity planning, and the definition of access control requirements and human resource policies
B. Security policy implementation, assignment of roles and responsibilities, and information asset classification
D. Senior management organizational structure, message distribution standards, and procedures for the operation of security management systems
Card 234
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #11
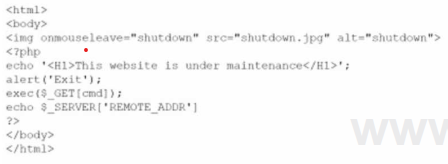
A company brings in a consultant to make improvements to its website. After the consultant leaves a web developer notices unusual activity on the website and submits a suspicious file containing the following code to the security team:
Which of the following did the consultant do?
Answer
A. Implanted a backdoor
B. Implemented privilege escalation
C. Implemented clickjacking
D. Patched the web server
Card 235
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #12
Which of the following makes STIX and OpenloC information readable by both humans and machines?
Answer
C. OVAL
A. XML
D. TAXII
B. URL
Card 236
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #15
Which of the following is the first step that should be performed when establishing a disaster recovery plan?
Answer
B. Determine the site to be used during a disaster C Demonstrate adherence to a standard disaster recovery process
A. Agree on the goals and objectives of the plan
C. Identity applications to be run during a disaster
Card 237
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #16
A technician identifies a vulnerability on a server and applies a software patch. Which of the following should be the next step in the remediation process?
Answer
C. Validation
D. Rollback
B. Implementation
A. Testing
Card 238
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #20
When starting an investigation, which of the following must be done first?
Answer
C. Seize all related evidence
B. Secure the scene
A. Notify law enforcement
D. Interview the witnesses
Card 239
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #23
An analyst notices there is an internal device sending HTTPS traffic with additional characters in the header to a known-malicious IP in another country. Which of the following describes what the analyst has noticed?
Answer
A. Beaconing
C. Buffer overflow
B. Cross-site scripting
D. PHP traversal
Card 240
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #24
A security analyst is reviewing a packet capture in Wireshark that contains an FTP session from a potentially compromised machine. The analyst sets the following display filter: ftp. The analyst can see there are several RETR
requests with 226 Transfer complete responses, but the packet list pane is not showing the packets containing the file transfer itself. Which of the following can the analyst perform to see the entire contents of the
downloaded files?
Answer
D. Navigate to the File menu and select FTP from the Export objects option
C. Change the display filter to f cp-daca and follow the TCP streams
B. Change the display filter to tcg.port=20
A. Change the display filter to f cp. accive. pore
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.