All questions without description (e.g. Question #1) are from the premium version of Exam Topics. I always choosed the community answer if possible for them. The rest is from the specific documents, written in the header of each question.
A company that has a geographically diverse workforce and dynamic IPs wants to implement a vulnerability scanning method with reduced network traffic. Which of the following would best meet this requirement?
Answer
A. External
B. Agent-based
D. Credentialed
C. Non-credentialed
Card 242
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #33
There are several reports of sensitive information being disclosed via file sharing services. The company would like to improve its security posture against this threat. Which of the following security controls would best
support the company in this scenario?
Answer
B. Improve employee training and awareness
A. Implement step-up authentication for administrators
D. Deploy mobile device management
C. Increase password complexity standards
Card 243
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #34
Which of the following is the best way to begin preparation for a report titled 'What We Learned' regarding a recent incident involving a cybersecurity breach?
Answer
A. Determine the sophistication of the audience that the report is meant for
B. Include references and sources of information on the first page
D. Decide on the color scheme that will effectively communicate the metrics
C. Include a table of contents outlining the entire report
Card 244
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #42
During an incident, an analyst needs to acquire evidence for later investigation. Which of the following must be collected first in a computer system, related to its volatility level?
Answer
A. Disk contents
C. Temporary files
B. Backup data
D. Running processes
Card 245
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #48
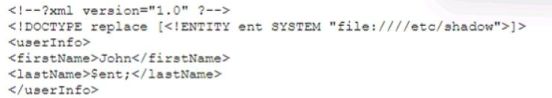
A security analyst is validating a particular finding that was reported in a web application vulnerability scan to make sure it is not a false positive. The security analyst uses the snippet below:
Which of the following vulnerability types is the security analyst validating?
Answer
D. SSRF
B. XSS
C. XXE
A. Directory traversal
Card 246
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #50
A security analyst is performing vulnerability scans on the network. The analyst installs a scanner appliance, configures the subnets to scan, and begins the scan of the network. Which of the following would be missing from a
scan performed with this configuration?
Answer
B. Registry key values
C. Open ports
A. Operating system version
D. IP address
Card 247
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #51
After updating the email client to the latest patch, only about 15% of the workforce is able to use email. Windows 10 users do not experience issues, but Windows 11 users have constant issues. Which of the following did the
change management team fail to do?
Answer
C. Rollback
D. Validation
A. Implementation
B. Testing
Card 248
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #52
The management team requests monthly KPI reports on the company's cybersecurity program. Which of the following KPIs would identify how long a security threat goes unnoticed in the environment?
Answer
A. Employee turnover
C. Mean time to detect
D. Level of preparedness
B. Intrusion attempts
Card 249
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #53
An incident response analyst is investigating the root cause of a recent malware outbreak. Initial binary analysis indicates that this malware disables host security services and performs cleanup routines on it infected hosts,
including deletion of initial dropper and removal of event log entries and prefetch files from the host. Which of the following data sources would most likely reveal evidence of the root cause?
(Select two)
Answer
B. Registry artifacts
A. Creation time of dropper
D. Prefetch files
C. EDR data
E. File system metadata
F. Sysmon event log
Card 250
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #54
During an incident, some loCs of possible ransomware contamination were found in a group of servers in a segment of the network. Which of the following steps should be taken next?
Answer
A. Isolation
D. Preservation
C. Reimaging
B. Remediation
Card 251
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #55
When investigating a potentially compromised host, an analyst observes that the process BGInfo.exe (PID 1024), a Sysinternals tool used to create desktop backgrounds containing host details, has bee running for over two
days. Which of the following activities will provide the best insight into this potentially malicious process, based on the anomalous behavior?
Answer
B. SMB network traffic related to the system process
A. Changes to system environment variables
D. Activities taken by PID 1024
C. Recent browser history of the primary user
Card 252
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #56
A vulnerability scan of a web server that is exposed to the internet was recently completed. A security analyst is reviewing the resulting vector strings:
Which of the following vulnerabilities should be patched first?
Answer
B. Vulnerability 2
C. Vulnerability 3
A. Vulnerability 1
D. Vulnerability 4
Card 253
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #57
A Chief Information Security Officer (CISO) wants to disable a functionality on a business-critical web application that is vulnerable to RCE in order to maintain the minimum risk level with minimal increased cost.
Which of the following risk treatments best describes what the CISO is looking for?
Answer
B. Mitigate
D. Avoid
C. Accept
A. Transfer
Card 254
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #62
An organization was compromised, and the usernames and passwords of all em-ployees were leaked online. Which of the following best describes the remedia-tion that could reduce the impact of this situation?
Answer
A. Multifactor authentication
B. Password changes
C. System hardening
D. Password encryption
Card 255
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #63
An organization would like to ensure its cloud infrastructure has a hardened configuration. A requirement is to create a server image that can be deployed with a secure template. Which of the following is the best resource to
ensure secure configuration?
Answer
A. CIS Benchmarks
C. OWASP Top Ten
D. ISO 27001
B. PCI DSS
Card 256
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #65
Which of the following threat-modeling procedures is in the OWASP Web Security Testing Guide?
Answer
D. Security by design
A. Review Of security requirements
B. Compliance checks
C. Decomposing the application
Card 257
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #66
Which of the following is a reason why proper handling and reporting of existing evidence are important for the investigation and reporting phases of an incident response?
Answer
D. To prevent the possible loss of a data source for further root cause analysis
B. To present a lessons-learned analysis for the incident response team
C. To ensure the evidence can be used in a postmortem analysis
A. TO ensure the report is legally acceptable in case it needs to be presented in court
Card 258
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #67
A Chief Information Security Officer (CISO) is concerned that a specific threat actor who is known to target the company's business type may be able to breach the network and remain inside of it for an extended period of
time.
Which of the following techniques should be performed to meet the CISO's goals?
Answer
A. Vulnerability scanning
B. Adversary emulation
D. Bug bounty
C. Passive discovery
Card 259
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #68
While performing a dynamic analysis of a malicious file, a security analyst notices the memory address changes every time the process runs. Which of the following controls is most likely preventing the analyst from finding
the proper memory address of the piece of malicious code?
Answer
A. Address space layout randomization
C. Stack canary
B. Data execution prevention
D. Code obfuscation
Card 260
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #71
A security analyst is reviewing the findings of the latest vulnerability report for a company's web application. The web application accepts files for a Bash script to be processed if the files match a given hash. The analyst is able to submit files to the system due to a hash collision. Which of the following should the analyst suggest to mitigate the vulnerability with the fewest changes to the current script and infrastructure?
Answer
B. Replace the current MD5 with SHA-256.
D. Replace the MD5 with digital signatures.
A. Deploy a WAF to the front of the application.
C. Deploy an antivirus application on the hosting system.
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.