All questions without description (e.g. Question #1) are from the premium version of Exam Topics. I always choosed the community answer if possible for them. The rest is from the specific documents, written in the header of each question.
The SOC received a threat intelligence notification indicating that an employee's credentials were found on the dark web. The user's web and log-in activities were reviewed for malicious or anomalous connections, data uploads/downloads, and exploits. A review of the controls confirmed multifactor authentication was enabled.
Which of the following should be done first to mitigate impact to the business
networks and assets?
Answer
A. Perform a forced password reset.
B. Communicate the compromised credentials to the user.
C. Perform an ad hoc AV scan on the user's laptop.
D. Review and ensure privileges assigned to the user's account reflect least privilege.
E. Lower the thresholds for SOC alerting of suspected malicious activity.
Card 282
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #34
When undertaking a cloud migration of multiple SaaS application, an organizations system administrator struggled … identity and access management to cloud-based assets. Which of the following service models would have reduced the complexity of this project?
Answer
A. CASB
C. ZTNA
B. SASE
D. SWG
Card 283
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #38
An employee downloads a freeware program to change the desktop to the classic look of legacy Windows. Shortly after the employee installs the program, a high volume of random DNS queries begin to originate from the system. An investigation on the system reveals the following:
During normal security monitoring activities, the following activity was observed:
cd C:\Users\Documents\HR\Employees
takeown/f .*
SUCCESS:
Which of the following best describes the potentially malicious activity observed?
Answer
B. Data exfiltration
A. Registry changes or anomalies
D. File configuration changes
C. Unauthorized privileges
Card 285
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #41
Which of the following would eliminate the need for different passwords for a variety or internal application?
Answer
A. CASB
D. MFA
B. SSO
C. PAM
Card 286
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #43
During a recent site survey. an analyst discovered a rogue wireless access point on the network. Which of the following actions should be taken first to protect the network while preserving evidence?
Answer
D. Disconnect the access point from the network
C. Identify who is connected to the access point and attempt to find the attacker.
A. Run a packet sniffer to monitor traffic to and from the access point.
B. Connect to the access point and examine its log files.
Card 287
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #45
Due to an incident involving company devices, an incident responder needs to take a mobile phone to the lab for further investigation. Which of the following tools should be used to maintain the integrity of the mobile phone while it is transported? (Select two).
Answer
C. Thumb Drive
A. Signal-shielded bag
B. Tamper-evident seal
D. Crime scene tape
E. Write blocker
F. Drive duplicator
Card 288
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #48
During a security test, a security analyst found a critical application with a buffer overflow vulnerability.
Which of the following would be best to mitigate the vulnerability at the application level?
Answer
A. Perform OS hardening.
D. Configure address space layout randomization.
B. Implement input validation.
C. Update third-party dependencies.
Card 289
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #52
Several critical bugs were identified during a vulnerability scan. The SLA risk requirement is that all critical vulnerabilities should be patched within 24 hours. After sending a notification to the asset owners, the patch cannot be deployed due to planned, routine system upgrades
Which of the following is the best method to remediate the bugs?
Answer
A. Reschedule the upgrade and deploy the patch
B. Request an exception to exclude the patch from installation
C. Update the risk register and request a change to the SLA
D. Notify the incident response team and rerun the vulnerability scan
Card 290
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #59
A security analyst found the following vulnerability on the company’s website:
Which of the following should be implemented to prevent this type of attack in the future?
Answer
C. Code obfuscation
B. Output encoding
A. Input sanitization
D. Prepared statements
Card 291
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #78
A systems administrator notices unfamiliar directory names on a production server. The administrator reviews the directory listings and files, and then concludes the server has been compromised. Which of the following steps should the administrator take next?
Answer
A. Inform the internal incident response team.
B. Follow the company's incident response plan.
D. Determine when the access started.
C. Review the lessons learned for the best approach.
Card 292
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #79
Which of the following is the most appropriate action a security analyst to take to effectively identify the most security risks associated with a locally hosted server?
Answer
D. Execute a vulnerability scan against the target host.
B. Contract an external penetration tester to attempt a brute-force attack.
C. Download a vendor support agent to validate drivers that are installed.
A. Run the operating system update tool to apply patches that are missing.
Card 293
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #82
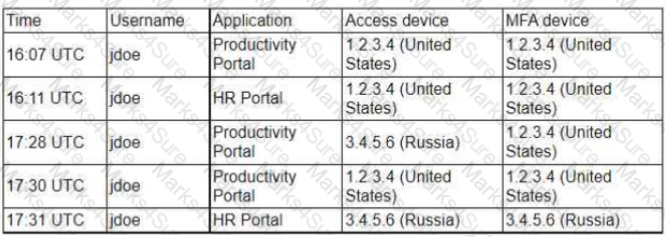
A security analyst received an alert regarding multiple successful MFA log-ins for a particular user When reviewing the authentication logs the analyst sees the following:
Which of the following are most likely occurring, based on the MFA logs? (Select two).
Answer
B. Push phishing
C. impossible geo-velocity
F. Password spray
E. Rogue access point
D. Subscriber identity module swapping
A. Dictionary attack
Card 294
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #88
A cybersecurity analyst has recovered a recently compromised server to its previous state. Which of the following should the analyst perform next?
Answer
C. Reporting
D. Forensic analysis
B. Isolation
A. Eradiction
Card 295
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #91
An analyst discovers unusual outbound connections to an IP that was previously blocked at the web proxy and firewall. Upon further investigation, it appears that the proxy and firewall rules that were in place were removed by a service account that is not recognized.
Which of the following parts of the Cyber Kill Chain does this describe?
Answer
C. Reconnaissance
A. Delivery
B. Command and Control
D. Weaporization
Card 296
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #92
An analyst is conducting monitoring against an authorized team that win perform adversarial techniques. The analyst interacts with the team twice per day to set the stage for the techniques to be used.
Which of the following teams is the analyst a member of?
Answer
A. Orange Team
C. Red Team
B. Blue Team
D. Purple Team
Card 297
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #93
An attacker recently gained unauthorized access to a financial institution's database, which contains confidential information. The attacker exfiltrated a large amount of data before being detected and blocked. A security analyst needs to complete a root cause analysis to determine how the attacker was able to gain access.
Which of the following should the analyst perform first?
Answer
A. Document the incident and any findings related to the attack for future reference.
C. Review the log files that record all events related to client applications and user access.
B. Interview employees responsible for managing the affected systems.
D. Identify the immediate actions that need to be taken to contain the incident and minimize damage.
Card 298
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #101
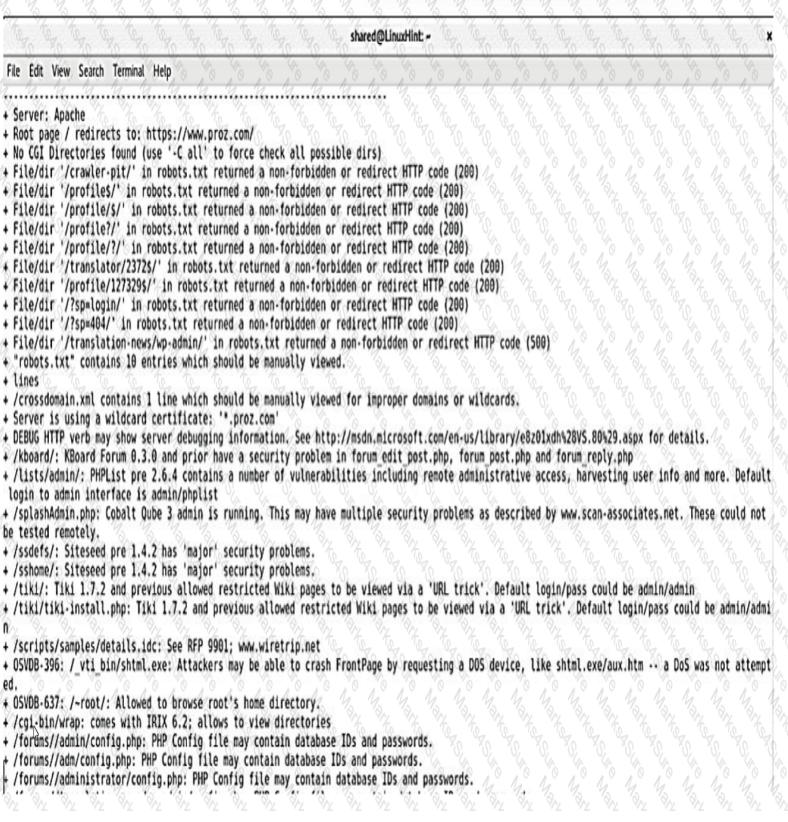
A security analyst reviews the following results of a Nikto scan: Which of the following should the security administrator investigate next?
Answer
B. phpList
A. tiki
C. shtml.exe
D. sshome
Card 299
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #106
While reviewing the web server logs a security analyst notices the following snippet
..\../..\../boot.ini
Which of the following is being attempted?
Answer
C. Cross-site scripting
E. Enumeration of/etc/password
D. Remote code execution
A. Directory traversal
B. Remote file inclusion
Card 300
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #109
Which of the following entities should an incident manager work with to ensure correct processes are adhered to when communicating incident reporting to the general public, as a best practice? (Select two)
Answer
A. Law enforcement
B. Governance
E. Public relations
D. Manager
C. Legal
F. Human resources
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.
 Which of the following are most likely occurring, based on the MFA logs? (Select two).
 Which of the following should the security administrator investigate next?