All questions without description (e.g. Question #1) are from the premium version of Exam Topics. I always choosed the community answer if possible for them. The rest is from the specific documents, written in the header of each question.
During an internal code review, software called "ACE" was discovered to have a vulnerability that allows the execution of arbitrary code. The vulnerability is in a legacy, third-party vendor resource that is used by the ACE software. ACE is used worldwide and is essential for many businesses in this industry. Developers informed the Chief Information Security Officer that removal of the vulnerability will take time.
Which of the following is the first action to take?
Answer
A. Look for potential loCs in the company.
C. Remove the affected vendor resource from the ACE software.
D. Develop a compensating control until the issue can be fixed permanently.
B. Inform customers of the vulnerability.
Card 302
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #116
During an incident, a security analyst discovers a large amount of Pll has been emailed externally from an employee to a public email address. The analyst finds that the external email is the employee's personal email.
Which of the following should the analyst recommend be done first?
Answer
A. Place a legal hold on the employee's mailbox.
D. Configure a deny rule on the firewall.
C. Disable the public email access with CASB.
B. Enable filtering on the web proxy.
Card 303
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #118
A company has a primary control in place to restrict access to a sensitive database. However, the company discovered an authentication vulnerability that could bypass this control. Which of the following is the best compensating control?
Answer
A. Running regular penetration tests to identify and address new vulnerabilities
B. Conducting regular security awareness training of employees to prevent social engineering attacks
C. Deploying an additional layer of access controls to verify authorized individuals
D. Implementing intrusion detection software to alert security teams of unauthorized access attempts
Card 304
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #129
An organization is conducting a pilot deployment of an e-commerce application. The application's source code is not available. Which of the following strategies should an analyst recommend to evaluate the security of the software?
Answer
C. Dynamic testing
A. Static testing
B. Vulnerability testing
D. Penetration testing
Card 305
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #138
The Chief Executive Officer (CEO) has notified that a confidential trade secret has been compromised. Which of the following communication plans should the CEO initiate?
Answer
A. Alert department managers to speak privately with affected staff.
B. Schedule a press release to inform other service provider customers of the compromise.
C. Disclose to all affected parties in the Chief Operating Officer for discussion and resolution.
D. Verify legal notification requirements of PII and SPII in the legal and human resource departments.
Card 306
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #141
A security analyst recently used Arachni to perform a vulnerability assessment of a newly developed web application. The analyst is concerned about the following output:
[+] XSS: In form input 'txtSearch' with action https://localhost/search.aspx
[-] XSS: Analyzing response #1...
[-] XSS: Analyzing response #2...
[-] XSS: Analyzing response #3...
[+] XSS: Response is tainted. Looking for proof of the vulnerability.
Which of the following is the most likely reason for this vulnerability?
Answer
D. The developer did not set proper cross-site request forgery protections.
A. The developer set input validation protection on the specific field of search.aspx.
B. The developer did not set proper cross-site scripting protections in the header.
C. The developer did not implement default protections in the web application build.
Card 307
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #144
A security analyst noticed the following entry on a web server log:
Warning:
fopen (http://127.0.0.1:16) : failed to open stream:
Connection refused in /hj/var/www/showimage.php on line 7
Which of the following malicious activities was most likely attempted?
Answer
B. CSRF
A. XSS
C. SSRF
D. RCE
Card 308
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #156
Which of the following statements best describes the MITRE ATT&CK framework?
Answer
A. It provides a comprehensive method to test the security of applications.
E. It breaks down intrusions into a clearly defined sequence of phases.
C. It helps identify and stop enemy activity by highlighting the areas where an attacker functions.
B. It provides threat intelligence sharing and development of action and mitigation strategies.
D. It tracks and understands threats and is an open-source project that evolves.
Card 309
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #157
A security analyst detects an email server that had been compromised in the internal network. Users have been reporting strange messages in their email inboxes and unusual network traffic. Which of the following incident response steps should be performed next?
Answer
A. Preparation
D. Eradiction
B. Validation
C. Containment
Card 310
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #164
Exploit code for a recently disclosed critical software vulnerability was publicly available (or download for several days before being removed. Which of the following CVSS v.3.1 temporal metrics was most impacted by this exposure?
Answer
C. Report confidence
D. Availability
B. Exploit code maturity
A. Remediation Level
Card 311
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #165
An organization discovered a data breach that resulted in Pll being released to the public. During the lessons earned review, the panel identified discrepancies regarding who was responsible for external reporting, as well as the timing requirements. Which of the following actions would best address the reporting issue?
Answer
C. Defining which security incidents require external notifications and incident reporting in addition to internal stakeholders
A. Creating a playbook denoting specific SLAs and containment actions per incident type
B. Researching federal laws, regulatory compliance requirements, and organizational policies to document specific reporting SLAs
D. Designating specific roles and responsibilities within the security team and stakeholders to streamline tasks
Card 312
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #169
An analyst reviews a recent government alert on new zero-day threats and finds the following CVE metrics for the most critical of the vulnerabilities:
Which of the following represents the exploit code maturity of this critical vulnerability?
Answer
B. S:C
A. E:U
C. RC:R
D. AV:N
E. AC:L
Card 313
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #171
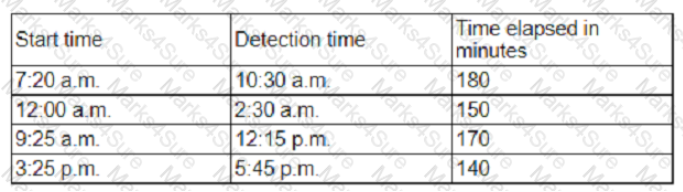
An organization has tracked several incidents that are listed in the following table:
Which of the following is the organization's MTTD?
Answer
D. 180
C. 160
B. 150
A. 140
Card 314
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #172
A security analyst would like to integrate two different SaaS-based security tools so that one tool can notify the other in the event a threat is detected. Which of the following should the analyst utilize to best accomplish this goal?
Answer
B. API endpoint
D. SNMP trap
A. SMB share
C. SMTP notification
Card 315
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #176
AXSS vulnerability was reported on one of the non-sensitive/non-mission-critical public websites of a company. The security department confirmed the finding and needs to provide a recommendation to the application owner.
Which of the following recommendations will best prevent this vulnerability from being exploited? (Select two).
Answer
A. Implement an IPS in front of the web server.
B. Enable MFA on the website.
E. Configure TLS v1.3 on the website.
F. Fix the vulnerability using a virtual patch at the WAF.
D. Implement a compensating control in the source code.
C. Take the website offline until it is patched.
Card 316
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #177
An attacker has just gained access to the syslog server on a LAN. Reviewing the syslog entries has allowed the attacker to prioritize possible next targets. Which of the following is this an example of?
Answer
C. Service port identification
A. Passive network foot printing
D. Application versioning
B. OS fingerprinting
Card 317
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #178
A security analyst is working on a server patch management policy that will allow the infrastructure team to be informed more quickly about new patches. Which of the following would most likely be required by the infrastructure team so that vulnerabilities can be remediated quickly? (Select two).
Answer
A. Hostname
B. Missing KPI
F. npm identifier
E. loCs
D. POC availability
C. CVE details
Card 318
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #179
Which of the following would likely be used to update a dashboard that integrates…..
Answer
B. Extensible Markup Language
A. Webhooks
C. Threat feed combination
D. JavaScript Object Notation
Card 319
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #180
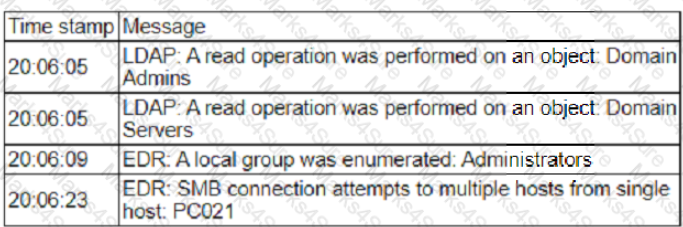
A security analyst is reviewing events that occurred during a possible compromise. The analyst obtains the following log:
Which of the following is most likely occurring, based on the events in the log?
Answer
A. An adversary is attempting to find the shortest path of compromise.
B. An adversary is performing a vulnerability scan.
D. An adversary is performing a password stuffing attack.
C. An adversary is escalating privileges.
Card 320
Question
CompTIA-CS0-003 ,27.01.24-unlocked.pdf
Question #182
A security analyst has prepared a vulnerability scan that contains all of the company's functional subnets. During the initial scan, users reported that network printers began to print pages that contained unreadable text and icons.
Which of the following should the analyst do to ensure this behavior does not oocur during subsequent vulnerability scans?
Answer
A. Perform non-credentialed scans.
D. Increase the threshold length of the scan timeout.
C. Create a tailored scan for the printer subnet.
B. Ignore embedded web server ports.
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.