351. An air traffic controller receives a change to the flight plan for an aircraft in the morning over the telephone. The air traffic controller compares the change with what appears on the radar and realizes that the information is incorrect. As a result, the air traffic controller can prevent an event.
Which of the following of the following examples is this scenario based on?
Answer
Vishing
SPIM attack
Unsecure VolP protocols
Mobile Hijacking
Card 22
Question
352. A company has numerous employees who store PHI data locally on devices. The Chief Information Officer wants to implement a solution to reduce external exposure of PHI but not affect the business. The first step the IT team should perform is to deploy a DLP solution:
Answer
in blocking mode
in monitoring mode.
for only data at reset.
for only data in transit.
Card 23
Question
353. A security analyst needs to recommend a solution that will allow current Active Directory accounts and groups to be used for access controls on both network and remote-access devices.
Which of the following should the analyst recommend? (Select two).
Answer
Kerberos
OpenID
CHAP
OAuth
RADIUS
TACACS+
Card 24
Question
354. A security analyst is investigating a report from a penetration test. During the penetration test, consultants were able to download sensitive data from a back-end server. The back-end server was exposing an API that should have only been available from the company's mobile application. After reviewing the back-end server logs, the security analyst finds the following entries:
Which of the following is the most likely cause of the security control bypass?
Answer
WAF bypass
User-agent spoofing
IP address allow list
Referrer manipulation
Card 25
Question
355. A security analyst is assisting a team of developers with best practices for coding. The security analyst would like to defend against the use of SQL injection attacks. Which of the following should the security analyst recommend first?
Answer
Tokenization
Code signing
Secure cookies
Input validation
Card 26
Question
356. An employee's company email is configured with conditional access and requires that MFA is enabled and used. An example of MFA is a phone call and:
Answer
a push notification
a password
an authentication application
an SMS message.
Card 27
Question
357. Security engineers are working on digital certificate management with the top priority of making administration easier. Which of the following certificates is the best option?
Answer
User
Wildcard
Self-signed
Root
Card 28
Question
358. A company policy requires third-party suppliers to self-report data breaches within a specific time frame.
Which of the following third-party risk management policies is the company complying with?
Answer
SLA
EOL
NDA
MOU
Card 29
Question
359. A security administrator is using UDP port 514 to send a syslog through an unsecure network to the SIEM server. Which of the following is the best way for the administrator to improve the process?
Answer
Change the protocol to TCP.
Use a VPN from the internal server to the SIEM and enable DLP.
Add SSL/TLS encryption and use a TCP 6514 port to send logs.
Add LDAP authentication to the SIEM server.
Card 30
Question
360. A security engineer is investigating a penetration test report that states the company website is vulnerable to a web application attack. While checking the web logs from the time of the test, the engineer notices several invalid web form submissions using an unusual address:
"SELECT* FROM customername".
Which of the following is most likely being attempted?
Answer
Directory traversal
SQL injection
Privilege escalation
Cross-site scripting
Card 31
Question
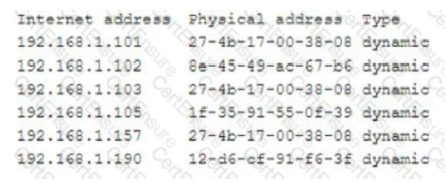
361. A security analyst is investigating network issues between a workstation and a company server.The workstation and server occasionally experience service disruptions, and employees are forced to reconnect to the server. In addition, some reports indicate sensitive information is being eaked from the server to the public. The workstation IP address is 192.168.1.103, and the server IP address is 192.168.1.101. The analyst runs arp -a On a separate workstation and obtains the following results:
Which of the following is most likely occurring?
Answer
Evil twin attack
MAC flooding attack
On-path attack
Domain hijacking attack
Card 32
Question
362. A Security engineer needs to implement an MDM solution that complies with the corporate mobile device policy. The policy states that in order for mobile users to access corporate resources on their devices, the following requirements must be met: Mobile device OSs must be patched up to the latest release. A screen lock must be enabled (passcode or biometric). Corporate data must be removed if the device is reported lost or stolen. Which of the following controls should the security engineer configure? (Select two).
Answer
Full device encryption
Storage segmentation
Geofencing
Disable firmware over-the-air
Remote wipe
Posture checking
Card 33
Question
363. A security analyst received the following requirements for the deployment of a security camera
solution:
- The cameras must be viewable by the on-site security guards.
- The cameras must be able to communicate with the video storage server.
- The cameras must have the time synchronized automatically.
- The cameras must not be reachable directly via the internet.
- The servers for the cameras and video storage must be available for remote maintenance via the company VPN.
Which of the following should the security analyst recommend to securely meet the remote connectivity requirements?
Answer
Creating firewall rules that prevent outgoing traffic from the subnet the servers and cameras reside on
Disabling all unused ports on the switch that the cameras are plugged into and enabling MAC filtering
Deploying a jump server that is accessible via the internal network that can communicate with the servers
Implementing a WAF to allow traffic from the local NTP server to the camera server
Card 34
Question
364. Several users have been violating corporate security policy by accessing inappropriate Sites on corporate-issued mobile devices while off campus. The senior leadership team wants all mobile devices to be hardened with controls that:
Limit the sites that can be accessed. Only allow access to internal resources while physically on campus. Restrict employees from downloading images from company email Whip of the following controls would best address this situation? (Select two).
Answer
Biometric authentication
MFA
GPS tagging
Screen lock and PIN requirements
Content management
Geofencing
Card 35
Question
365. A security team is conducting a security review of a hosted data provider. The management team has asked the hosted data provider to share proof that customer data is being appropriately protected. Which of the following would provide the best proof that customer data is being protected?
Answer
CSA
CSF
SOC2
ISO 31000
Card 36
Question
A company is moving to new location. The systems administrator has provided the following server
room requirements to the facilities staff:
- Consistent power levels in case of brownouts or voltage spikes
- A minimum of 30 minutes runtime following a power outage
- Ability to trigger graceful shutdowns of critical systems.
Which of the following would BEST meet the requirements?
Answer
Maintaining a standby, gas-powered generator
Using large surge suppressors on computer equipment
Deploying an appropriately sized, network-connected UPS device
Configuring managed PDUs to monitor power levels
Card 37
Question
367. Which of the following would most likely include language prohibiting end users from accessing personal email from a company device?
Answer
SLA
AUP
NDA
BPA
Card 38
Question
368. Which of the following describes software on network hardware that needs to be updated on a routine basis to help address possible vulnerabilities?
Answer
Vanishing
Firmware
Vendor management
Application programming interface
Encryption strength
Card 39
Question
369. Which of the following would be best to ensure data is saved to a location on a server, is easily scaled, and is centrally monitored?
Answer
Edge computing
Microservices
Thin client
Containers
Card 40
Question
370. A penetration tester was able to compromise a host using previously captured network traffic.
Which of the following is the result of this action?
Answer
Memory leak
Race condition
Replay attack
Integer overflow
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.