371. An organization needs to implement more stringent controls over administrator/root credentials and service accounts. Requirements for the project include:
* Check-in/checkout of credentials
* The ability to use but not know the password
* Automated password changes
* Logging of access to credentials
Which of the following solutions would meet the requirements?
Answer
OAuth 2.0
A privileged access management system
An OpenID Connect authentication system
Secure Enclave
Card 42
Question
372. The application development team is in the final stages of developing a new healthcare application. The team has requested copies of current PHI records to perform the final testing.
Which of the following would be the best way to safeguard this information without impeding the testing process?
Answer
Installing a FIM on the application server
Deploying DLP tools
Anonymizing the data
Implementing a content filter
Card 43
Question
373. The alert indicates an attacker entered thousands of characters into the text box of a web form. The web form was intended for legitimate customers to enter their phone numbers.
Which of the attacks has most likely occurred?
Answer
Resource exhaustion
Cross-Site Scripting (XSS)
Buffer Overflow (Pufferüberlauf)
Privilege Escalation (Berechtigungserweiterung)
Card 44
Question
374. A security administrator recently used an internal CA to issue a certificate to a public application. A user tries to reach the application but receives a message stating, "Your connection is not private."
Which of the following is the best way to fix this issue?
Answer
Install the certificate on each endpoint that needs to use the application
Send a CSR to a known CA and install the signed certificate on the application's server.
Send the new certificate to the users to install on their browsers.
Ignore the warning and continue to use the application normally.
Card 45
Question
375. A network security manager wants to implement periodic events that will test the security team's preparedness for incidents in a controlled and scripted manner, Which of the following concepts describes this scenario?
Answer
Tabletop exercise
Red-team exercise
Functional exercise
Business continuity plan testing
Card 46
Question
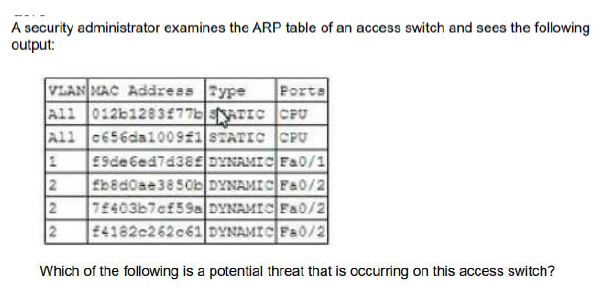
376.
Answer
MAC flooding on Fa0/2 port
DNS poisoning on port Fa0/1
ARP poisoning Fa0/1 port
DDoSonFa02 port
Card 47
Question
377. An engineer wants to inspect traffic to a cluster of web servers in a cloud environment.
Which of the following solutions should the engineer implement? (Select two).
Answer
WAF
TLS
DAST
Load balancer
CASB
VPN
Card 48
Question
378. A backup operator wants to perform a backup to enhance the RTO and RPO in a highly time- and storage-efficient way that has no impact on production systems.
Which of the following backup types should the operator use?
Answer
Tape
Snapshot
Image
Full
Card 49
Question
379. A company is developing a new initiative to reduce insider threats. Which of the following should the company focus on to make the greatest impact?
Answer
Least privilege
Social media analysis
Mandatory vacation
Nondisclosure agreements
Card 50
Question
380. Security analysts have noticed the network becomes flooded with malicious packets at specific times of the day. Which of the following should the analysts use to investigate this issue?
Answer
Correlation dashboards
Web metadata
System files
Bandwidth monitors
Card 51
Question
381. An organization decided not to put controls in place because of the high cost of implementing the controls compared to the cost of a potential fine.
Which of the following risk management strategies is the organization following?
Answer
Acceptance
Avoidance
Mitigation
Transference
Card 52
Question
382. Which of the following is the correct order of evidence from most to least volatile in forensic analysis?
Answer
CPU cache, temporary filesystems, memory, disk
CPU cache, memory, temporary filesystems, disk
CPU cache, memory, disk, temporary filesystems
Memory, disk, temporary filesystems, CPU cache
Card 53
Question
383. Which of the following is constantly scanned by internet bots and has the highest risk of attack in the case of the default configurations?
Answer
Wearable sensors
Real-time operating systems
Raspberry Pi
Surveillance systems
Card 54
Question
384. A security architect is designing a remote access solution for a business partner. The business partner needs to access one Linux server at the company. The business partner wants to avid managing a password for authentication and additional software installation.
Which of the following should the architect recommend?
Answer
Smart card
Soft token
SSH Key
CSR
Card 55
Question
385. Cloud security engineers are planning to allow and deny access to specific features in order to increase data security. Which of the following cloud features is the most appropriate to ensure access is granted properly?
Answer
Resource policies
Auditing
API integrations
Virtual networks
Card 56
Question
386. A building manager is concerned about people going in and out of the office during non-working hours.
Which of the following physical security controls would provide the best solution?
Answer
Bollards
Badges
Cameras
Locks
Card 57
Question
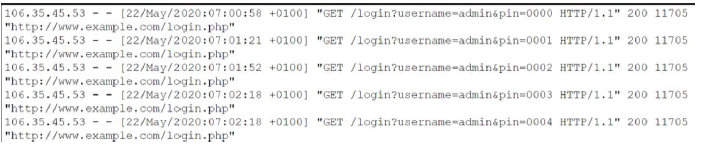
387. A security analyst is investigating what appears to be unauthorized access to a corporate web application. The security analyst reviews the web server logs and finds the following entries:
Which of the following password attacks is taking place?
Answer
Brute-force
Rainbow table
Spraying
Dictionary
Card 58
Question
388. A network penetration tester has successfully gained access to a target machine.
Which of the following should the penetration tester do next?
Answer
Move laterally to another machine.
Establish persistence for future use.
Exploit a zero-day vulnerability.
Clear the log files of all evidence
Card 59
Question
389. A security analyst is currently addressing an active cyber incident. The analyst has been able to identify affected devices that are running a malicious application with a unique hash.
Which of the following is the next step according to the incident response process?
Answer
Containment
Lessons learned
Recovery
Preparation
Card 60
Question
390. A web architect would like to move a company's website presence to the cloud. One of the management team's key concerns is resiliency in case a cloud provider's data center or network connection goes down.
Which of the following should the web architect consider to address this concern?
Answer
Segmentation
Virtual private cloud
Availability zones
Containers
How to use this set
Read the preview and check whether the content and answers suit your learning goal. You can add the public set to your sets to study it. Your account shows the available actions.